The first objection to hiring an offshore executive assistant is almost always security, and it is a fair one. You are about to give someone access to your calendar, inbox, CRM, and sometimes client or project data. The mistake is treating offshore executive assistant security as a leap of faith. Done properly, it is a documented checklist you can inspect line by line before a single credential changes hands.
Where you hire matters as much as how you onboard, because a managed agency and a freelance marketplace handle risk very differently, as our comparison of an offshore EA agency versus a freelance platform explains. This page lays out the full security onboarding checklist in plain language: the controls to require, how tiered access should work across the first 30 days, and the questions to ask any provider before you sign.
Is It Safe to Hire an Offshore Executive Assistant?
Yes, when security is treated as infrastructure rather than an afterthought. The risk with offshore executive assistants was never geography. It was providers who skip structure: shared logins, unmanaged laptops, and access handed over on day one with no record of what was granted. A safe setup replaces all of that with a defined process, so you know exactly what the assistant can reach, on what device, and since when. If a provider cannot hand you that in writing, that is the signal to keep looking, not a reason to rule out offshore hiring altogether.
The 5 Controls Every Offshore EA Onboarding Needs
Every credible offshore executive assistant security checklist rests on the same five controls. The assistant works from a managed device that you or the provider can monitor and wipe remotely. Every login lives in a password vault so credentials are never typed, texted, or emailed in plain view. A signed, enforceable NDA covers confidentiality and data handling before any access is granted. Access itself is tiered, expanding in stages rather than opening every system on day one. Finally, everything granted is logged, so you can audit exactly what the assistant can reach at any point and revoke it cleanly if the relationship ends. Miss any one of these and the rest of the setup is cosmetic.
Managed Devices and Vaulted Credentials
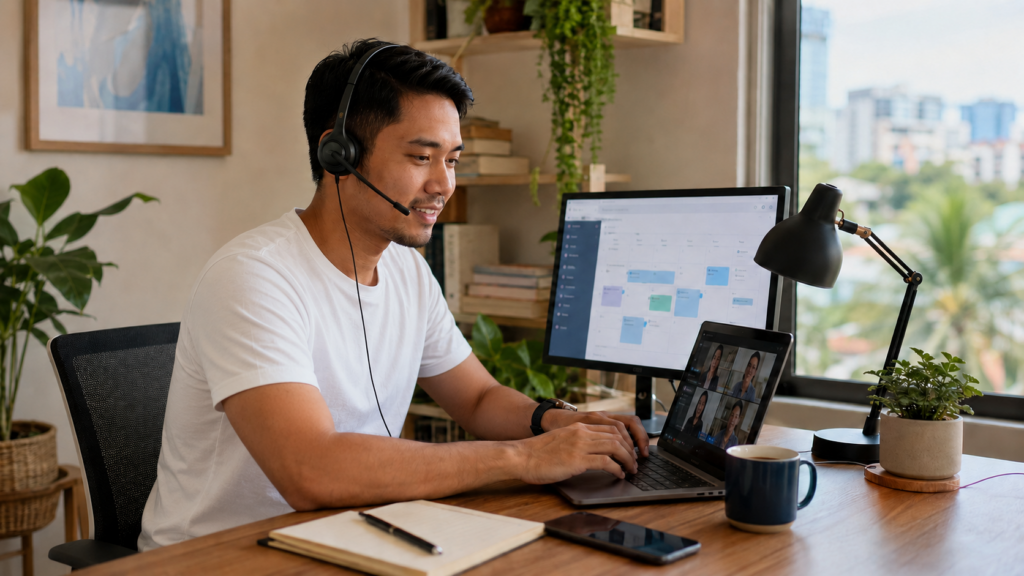
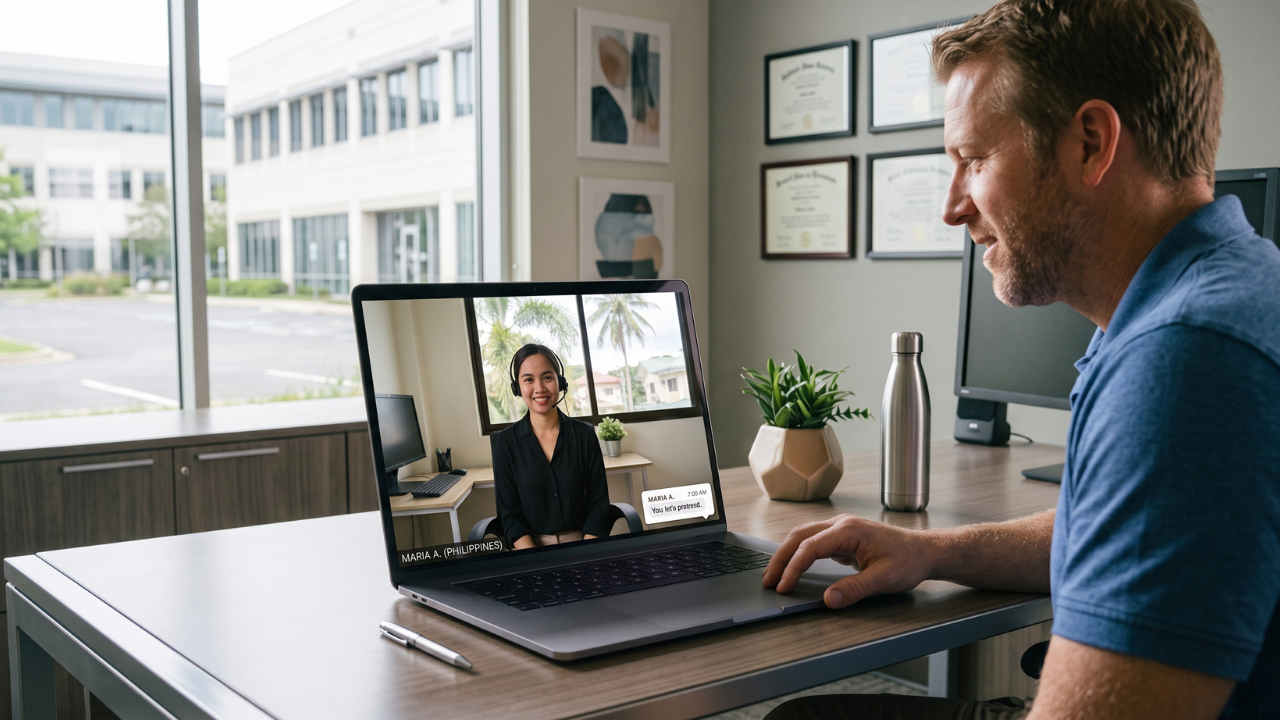
A managed device is the foundation, because it means the work happens on hardware your provider controls, not a personal laptop shared with family members or side projects. That device should support remote wipe and basic monitoring so a lost or compromised machine does not become a data exposure. Credential vaulting is the other half of the equation. A shared password manager lets the assistant log into your calendar, email, or CRM without ever seeing the raw password, and lets you revoke that access in seconds if needed. Together, a managed device and vaulted credentials mean a secure offshore executive assistant setup does not depend on trusting an individual’s home network or memory.
Tiered Access: Day 1, Week 1, Day 30
Access should never be all or nothing. On Day 1, the assistant typically gets calendar and email access, enough to start managing your time immediately. By Week 1, once initial work is reviewed, access can expand to project tools, reporting dashboards, or a CRM. By Day 30, with trust established and process documentation in place, the assistant can take on broader ownership, such as vendor communication or client facing scheduling. This staged model is also how a good provider handles onboarding an offshore EA into an existing ops or HR function, since it lets the assistant earn deeper system access as their judgment is proven rather than assumed upfront.
NDAs and Accountability
A verbal assurance of confidentiality is not a control, it is a hope. An enforceable NDA, signed before onboarding starts, should specifically address data handling, client information, and what happens to access and equipment if the engagement ends. Accountability also means knowing who at the provider is responsible if something goes wrong, not just the individual assistant. Ask whether the NDA is between you and the assistant, you and the agency, or both, and get clarity on that before day one rather than after an issue comes up.
The Security Onboarding Checklist (Copy and Save)
Before you sign with any offshore executive assistant provider, confirm the following five items are addressed in writing:
- A managed or monitored device is provisioned before day one.
- All credentials are stored in a password vault rather than shared directly.
- A signed, enforceable NDA is in place covering confidentiality and data handling.
- Access is granted in tiers across Day 1, Week 1, and Day 30, matched to the tools each stage actually requires.
- Every access grant is logged, giving you an inspectable record of what the assistant can reach and a clear process for revoking it.
A provider that can walk you through all five without hesitation is treating offshore data security as infrastructure, not an afterthought.
Questions to Ask Any Provider Before You Sign
A short conversation will tell you whether a provider takes offshore executive assistant security seriously. Ask what device the assistant will use and who owns it. Ask how credentials are stored and whether you will ever see a password in plain text. Ask what the NDA covers and who is bound by it. Ask how access is staged over the first 30 days and who decides when it expands. Ask what happens to access, devices, and data the day the engagement ends. Providers with a real process answer these in minutes. Providers without one talk around them.
Frequently Asked Questions
Is it safe to hire an offshore executive assistant?
Yes, when security is built into onboarding rather than added later. Safe placements use managed devices, vaulted credentials, signed NDAs, and access granted in stages instead of all at once. The clearest sign of a safe provider is a written security checklist you can review before you sign anything.
How do you securely onboard an offshore executive assistant?
Start before day one by provisioning a managed device and storing logins in a password vault the assistant never sees in plain text. Grant access in tiers at Day 1, Week 1, and Day 30, require a signed NDA, and log what the assistant can reach at each stage.
What security should an offshore EA provider have?
Require managed or monitored devices, credential vaulting so passwords are never shared directly, enforceable NDAs, and tiered, role based access. Ask how access is revoked when someone leaves and whether you can audit it. A credible provider hands you this as a checklist you can inspect, not a verbal assurance.
How do you protect credentials and data with an offshore assistant?
Use a password manager so the assistant logs in without ever seeing raw credentials, limit access to only the tools the role requires, and add multi factor authentication everywhere. Grant new access in stages as trust is established, and keep an inspectable record of what was granted and when.
Security You Can Inspect, Not Just Trust
Offshore does not mean unsafe. It means you need a provider who treats security as a documented process, not a promise. Managed devices, vaulted credentials, enforceable NDAs, and staged access give you an offshore executive assistant you can hand real work to on day one, with a record of exactly what they can reach and when. That is a standard you should be able to verify before you sign, and walk away with either way. If you are still deciding between a managed provider and a freelance marketplace, our guide to which model is safer is the place to start.
When you want to see the full security checklist and meet an EA who is device managed and NDA covered before day one, book a 15 minute fit call and you will leave with the checklist either way. See how our offshore executive assistant placements are built around this exact process.